Topic
Cyber Security
Everything we have published on Cyber Security — 22 articles.
Start here
Automate the Noticing, Not the Finding
A scanner finds vulnerabilities better than any script you will write. What no vendor knows is what your estate is supposed to look like — so automate change detection, and let git be the diffing engine.
More in Cyber Security
All Cyber Security articles
Git hooks for secrets: catching them locally, and enforcing it where it counts
A local hook is bypassed by --no-verify, lives outside the clone, and never sees a web commit. Set it up anyway, then put the real enforcement in CI and push protection — and rotate before you rewrite history.
OWASP Top 10 for LLM Applications 2026: what changed and how to test it
The 2026 edition landed on 3 August. Excessive Agency jumped from sixth to third, System Prompt Leakage was retired for the broader Hidden Context Exposure, and the ranking is now grounded in real incident data. Every category, with the tests that matter.
Build a port scanner in Python to understand what nmap is doing
A threaded and an asyncio TCP connect scanner, built from sockets — plus the limits that explain why nmap exists, and why a version banner is never proof of a vulnerability. Authorised targets only.
Is that online tool actually private? How to check before you paste a token
“Processed in your browser” is a claim about the tool's own code, not about the other scripts on the page. Four checks in order of what they prove — starting with the ten-second offline test that settles it.

Cyber Attack Statistics – Identifying Vulnerabilities and Strengthening Defenses
Cyber attacks are becoming more frequent, complex, and damaging. They can disrupt critical operations and damage infrastructure, including e-commerce and financial services. Hackers can also steal data and sell it on the Dark Web. This data can be used to identify users and compromise their security

Threat assessment: turning a vague worry into a ranked list
A threat assessment that produces a colour-coded grid nobody acts on has failed. A structured method, with the scoring made explicit and its limits stated.
What is OPSEC? Finding the indicators you are already leaking
OPSEC is not secrecy. It is working out which harmless-looking details add up to something an adversary can use, and which of them you are publishing without noticing.
Whaling attacks: executive impersonation and how to break the chain
Whaling targets the people who can authorise payments. It rarely involves malware, which is why technical controls miss it — and why the countermeasure is a process, not a filter.

Tailgating and piggybacking: physical access as an attack path
Following someone through a door defeats every network control at once. Why politeness is the vulnerability, and what actually stops it.

What is fuzzing? Coverage-guided testing that finds real bugs
Fuzzing means generating inputs a program was not expecting and watching what breaks. How coverage-guided fuzzers work, why sanitizers matter more than the fuzzer, and how to run one.

Cryptojacking: when someone else mines using your machines
Unauthorised mining rarely destroys anything, which is why it runs for months undetected. How it gets in, what it costs, and the signals that actually catch it.
Phishing and smishing: how they work and what actually stops them
Awareness training has never stopped a determined phishing campaign. What the attacks look like in 2026, why one-time codes are no longer enough, and the controls that work.
What is a CVE? How to read, search and act on vulnerability IDs
A CVE is a stable name for one vulnerability, not a severity score. How the identifiers are assigned, how they differ from CVSS, CWE and KEV, and how to decide which ones actually matter to you.
MFA explained: why not all second factors are equal
Multi-factor authentication is not one control. SMS codes, authenticator apps, push prompts and hardware keys fail in different ways — and only one resists phishing.
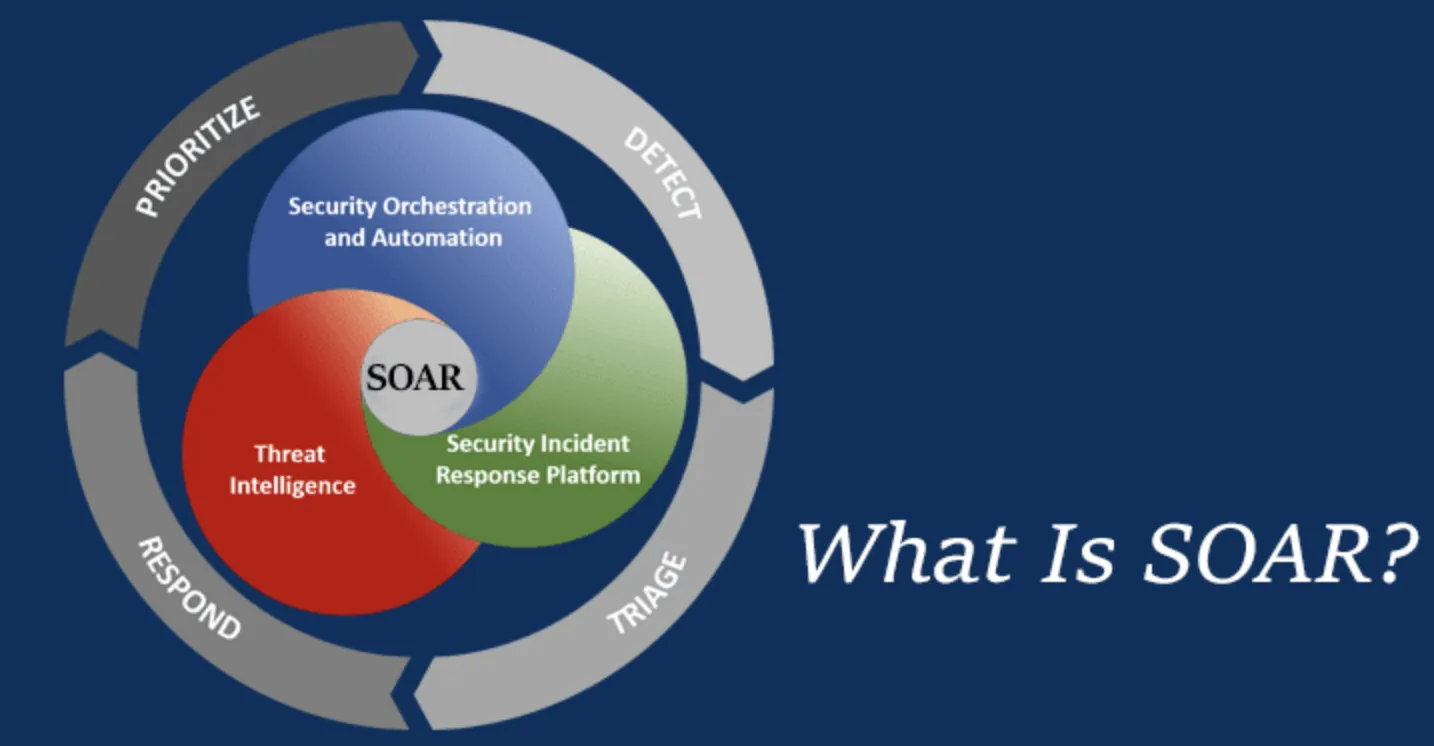
What is SOAR? Automating the response, not the decision
SOAR platforms automate the repetitive parts of incident response. Where they earn their cost, where they fail, and how they differ from SIEM and XDR.
Steps to Secure Your Server from Being Hacked
Securing a server from hacking is a critical task that requires a multi-layered approach. Here are some steps you can take to help protect your server: Keep software and operating systems up-to-date: Regularly applying software updates and patches can help close security holes and prevent vulnerabil
Top ways to enhance the Cyber security
The internet has made our life easier than ever by providing us with several benefits in today’s times. Unfortunately, along with the benefits that it offers, the internet is also filled up with several suspicious links and viruses. As a result, cyber-attacks are more common than ever. Globall